AI-driven social engineering attacks redefined cyber risk in 2025. From deepfake voices and cloned documents to coordinated attacks on private phones, messaging apps and supplier platforms, attackers now imitate real workflows and identities. Discover how these attacks unfold, why they work, and what organisations must prioritise next to stay secure.
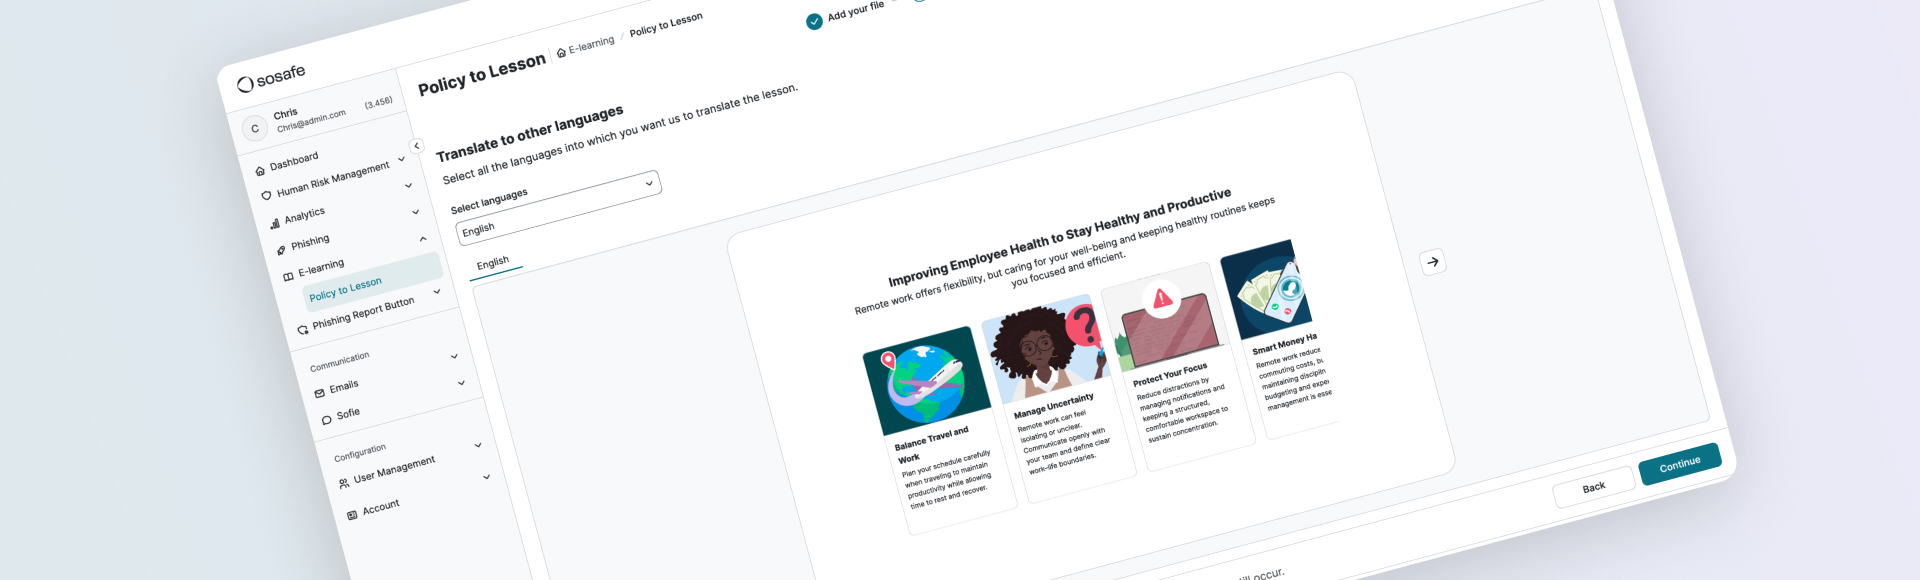
Policy management often ends with a PDF on an intranet and a trail of chased acknowledgements. But policies only reduce risk when employees understand what they mean in daily work. Learn how SoSafe Policy Management helps teams share updates in familiar channels, track acknowledgements centrally, and keep audit evidence ready.
The Zachman framework is one of the most established models in enterprise architecture. Here’s how it works, what it includes and how to apply it.
Data leakage protection, data leak prevention and data loss prevention are often used interchangeably, but they don’t mean the same thing. We untangle the terminology and outline strategies for CISOs.
Security is most likely to succeed when we speak the staff’s language, use relatable stories, and ease tasks into their daily routines. Empathy and clarity go a long way to prevent fatigue and burnout, and openly discussing mistakes and building small habits is how you cultivate a genuine security mindset. These human-centred strategies make training and culture stick together.

Artificial Intelligence is already influencing how employees think, create, and communicate, often in ways that unfold beyond leadership’s line of sight. By fostering awareness, curiosity, and ongoing learning, organisations can bridge the growing gap between what leaders believe they know about AI and how people are actually using it every day.
Shadow AI is the unsanctioned use of generative tools at work, and it’s already causing incredible financial and compliance harm, from regulatory penalties to costly breaches and bad decisions driven by hallucinations. This article explains what Shadow AI is, why it spreads faster than controls, what the risks look like, and a people-centred solution that security leaders can use.





 Reports
 Guides
 Blog
 Glossary
 Perks
 Customer stories
 Newsletter signup
 Webinars
 Replays
 Podcast
 All events
 Signal Security Summit
 Danger Lab
 Why SoSafe
 Careers
 News & press
 Contact
