HuFiCon
How to translate daily security operations into board-level budget
If your security team stops threats every day and shields the business from disaster, why does the executive committee still treat your department like an expensive cost centre?
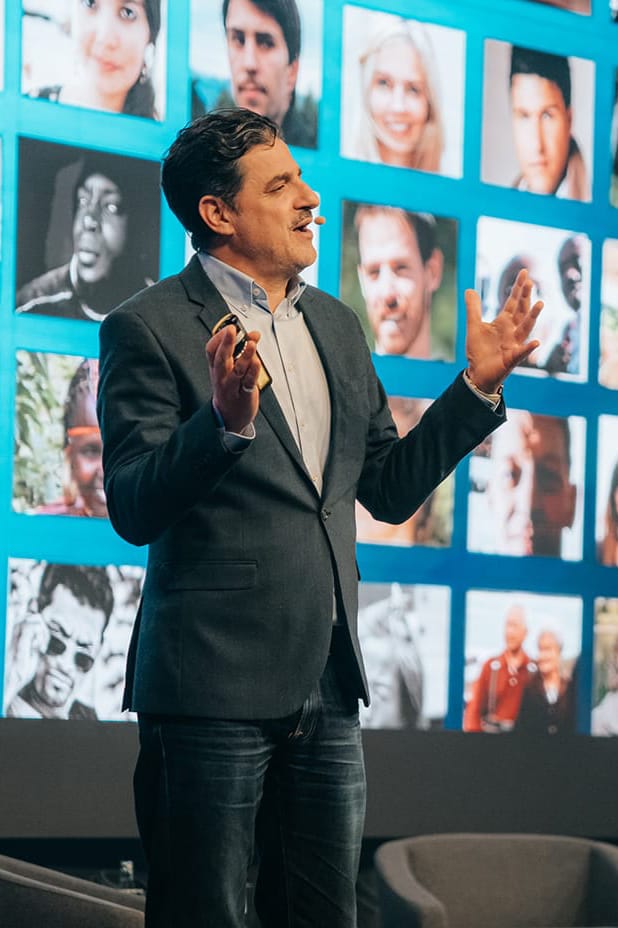
At HuFiCon 2025 (now the Signal Security Summit),Olaf Reimann, Senior Manager Enterprise Architecture & Cybersecurity Governance, BENTELER, addressed the daily grind inside high-stakes tech environments. He walked our audience through alert fatigue, relentless pressure, and team burnout, explaining how leaders must act as an operational umbrella so teams can deliver without burning out.
Protecting your team is a priority, but day-to-day support is only the starting point. Much like securing your own oxygen mask first, bringing the board alongside you is how you secure the resources your people need to thrive.
That is why Olaf is returning to the Signal Security Summit 2026 in Cologne, tackling both team care and boardroom influence across two sessions.
The problem with invisible success: why boards see zero risk
Security faces a frustrating paradox: when your team does its job right, nothing happens.
It is like the gym dilemma shared on our stage last year. People often quit after 3 months because the mirror does not show dramatic changes yet. In security, you harden infrastructure and keep systems online, but to an executive focused on return on capital, an absence of incidents looks like an absence of danger.
When security leaders try to close this gap, they often double down on activity data like patches deployed and blocked scans. To an executive, technical metrics easily sound like maintenance overhead.
Without business context, the pitch inevitably falls on deaf ears. A study by Walter Herbinger highlighted during our panel showed that communication, not technical depth, is the single biggest factor in a CISO’s success. Boards do not allocate capital based on CVE scores. They invest to protect business velocity, regulatory compliance, and supply chain continuity.
Turning technical debt into commercial leverage
Making the switch from technical metrics to business impact is a learned skill.
In his interactive masterclass, Storytelling für CISOs: Wie Security beim Board Gehör findet (conducted in German), Olaf Reimann joins Dr. Christian Reinhardt from SoSafe to walk through how to pitch security priorities without losing the room:
- Pitches that failed vs. pitches that worked: A direct look at presentations that died on the table compared to narratives that unlocked immediate funding.
- Translating technical debt: How to anchor legacy vulnerabilities and backlog strain directly to lost factory uptime and contract penalties.
- Peer sparring: Testing your narrative with other security leaders before stepping in front of your own board, and more.
Learn how to turn technical debt into executive decisions. Join us in Cologne on 18 November. Book your free spot.
Measuring human risk without vanity metrics
A strong narrative opens the door, but defensible metrics keep it open. Yet most human risk reporting relies on phishing click rates and training completion. These vanity metrics prove that employees checked a box, not that the company is safer. Worse, when teams face blame, employees sweep mistakes under the rug until an issue escalates into a crisis.
In the customer panel Proving impact: Measuring human risk and communicating value to the board, Olaf joins fellow practitioners Rian Redinger (Hörmann), Bastian Timmermann, and Joschka Havenith to share what works in practice:
- Metrics that matter: Replacing completion percentages with data that shows sustained behavioural change.
- Reporting speed: Using incident report times to prove that employees trust security enough to flag mistakes quickly.
- Executive dashboards: Structuring risk data so leadership immediately sees the return on investment.
If you are considering joining us, make sure this session is on your schedule. It is the fastest way to see what works in practice, straight from the people building it.
Move from defending your budget to driving business strategy: join us at the Signal Security Summit 2026
On 18 November 2026, the Signal Security Summit brings over 2,000 security leaders to Cologne.
Shielding your team from burnout only works when you have the executive backing to resource them properly. The Signal Security Summit gives you the space to step away from daily emergencies, learn how fellow CISOs secure boardroom buy-in, and return with the narrative tools you need to protect your team.
PS: If you can’t join us in Cologne on 18 November, you can still follow the discussions and hear directly from the experts on stage. The Signal Security Summit 2026 will also be available via livestream.
You might also be interested in:
 4 min read
Do you want to stay ahead of the cyber game?
Sign up for our newsletter to receive the latest cyber security articles, events, and resources. No spam, only content that truly matters.





 Reports
 Guides
 Blog
 Glossary
 Perks
 Customer stories
 Webinars
 Replays
 Podcast
 All events
 Signal Security Summit
 Danger Lab
 Careers
 News & press
 Contact
