FOR IT SERVICE AND CONSULTING COMPANIES
IT services cyber security for the people with access to your clients’ systems
- Security awareness training and phishing simulations for IT service companies
- Role-based lessons for admins, developers, the service desk and managers
- A programme aligned with NIS2 and ISO/IEC 27001 that reduces manual administration steps
How SoSafe helps
Solutions for your IT services cyber security risks
Campaigns without the manual work
Building phishing campaigns by hand takes time that smaller security teams rarely have. SoSafe’s behaviour-based email phishing simulations adjust difficulty and timing to how each person responds. For a scenario of your own, Simulation Studio with AI drafts a template from a prompt.
Lessons that fit each role and country
An administrator, a developer and a manager face different attacks. Role-based learning paths give each of them lessons that match their work, and the content is available in 34+ languages for teams spread across several countries.
Evidence beyond completion rates
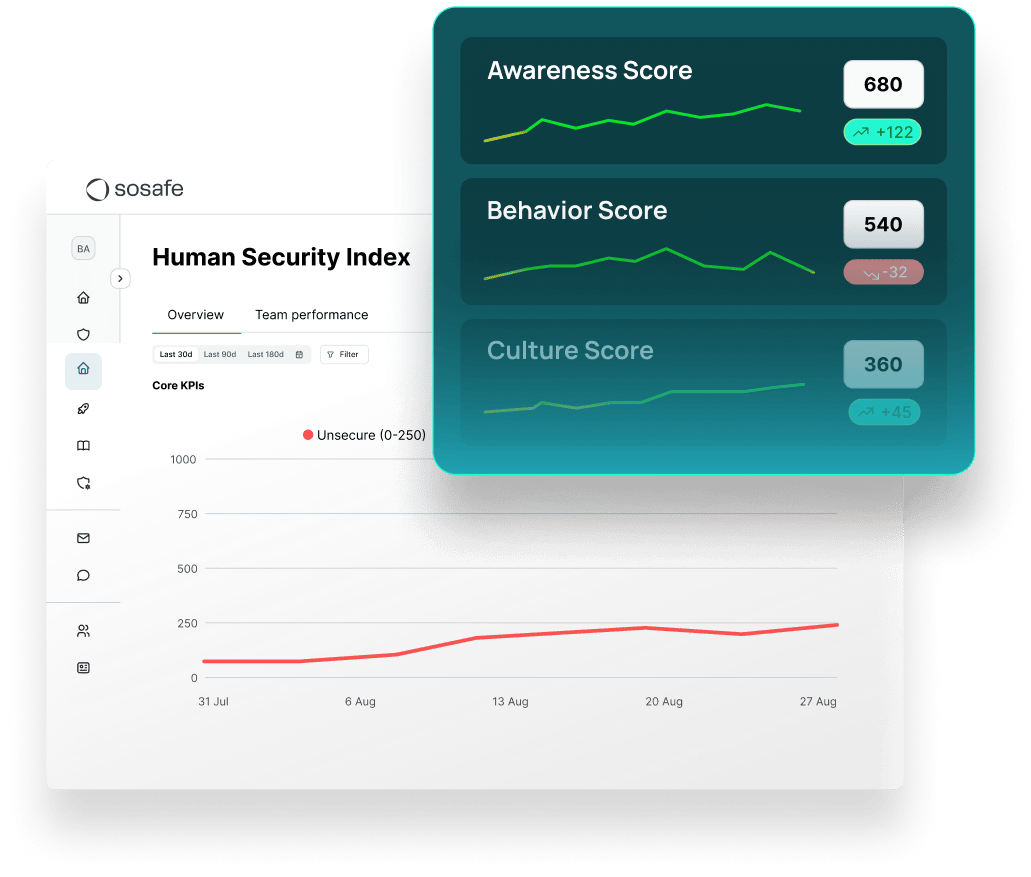
Auditors and clients want to know whether people act securely, not only whether they finished a course. The Human Security Index turns simulations, reported threats and learning progress into one figure you can follow across the year.
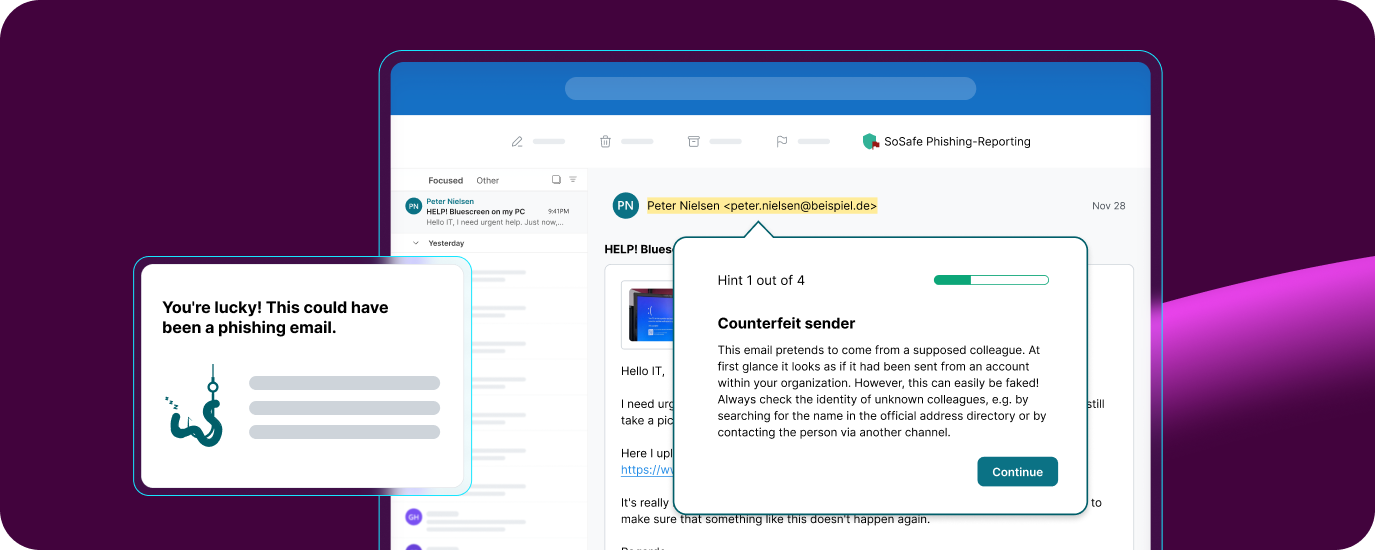
Campaigns without the manual work
Building phishing campaigns by hand takes time that smaller security teams rarely have. SoSafe’s behaviour-based email phishing simulations adjust difficulty and timing to how each person responds. For a scenario of your own, Simulation Studio with AI drafts a template from a prompt.
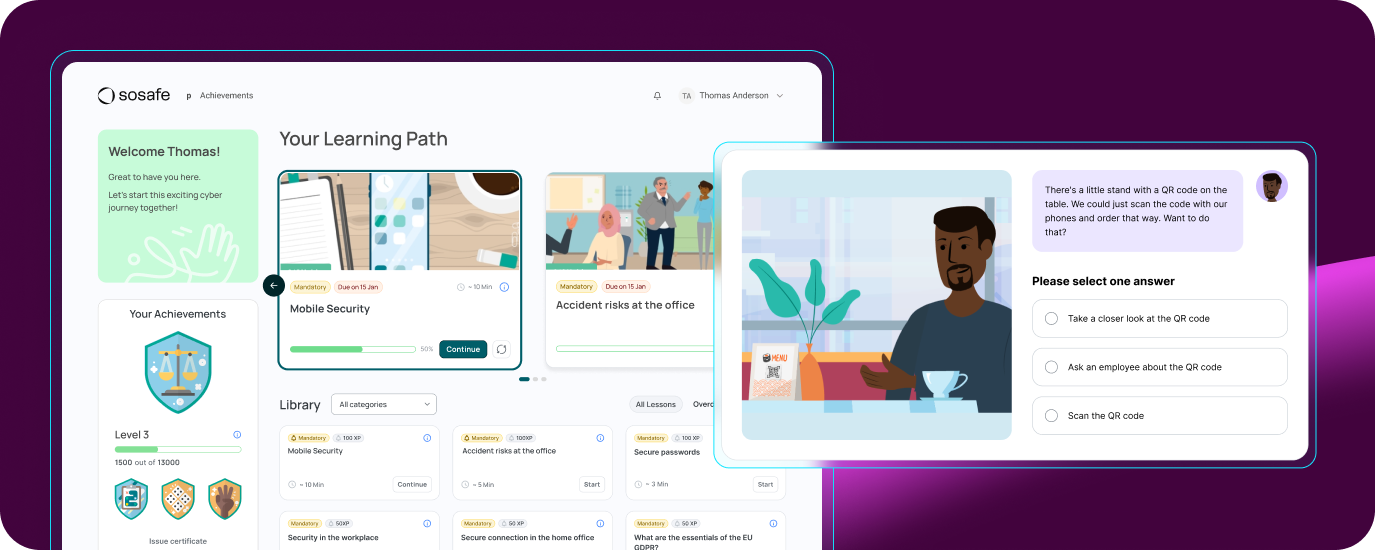
Lessons that fit each role and country
An administrator, a developer and a manager face different attacks. Role-based learning paths give each of them lessons that match their work, and the content is available in 34+ languages for teams spread across several countries.
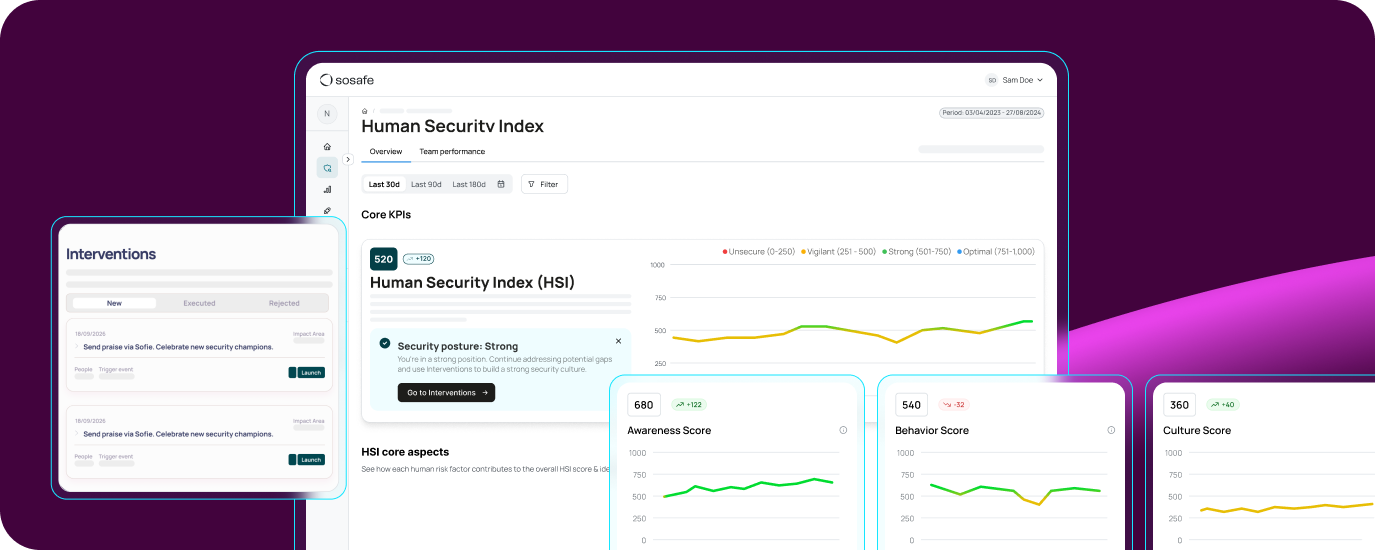
Evidence beyond completion rates
Auditors and clients want to know whether people act securely, not only whether they finished a course. The Human Security Index turns simulations, reported threats and learning progress into one figure you can follow across the year.
THE CHALLENGE
Where attacks on IT service companies usually begin
One account, many organisations
In its analysis of incidents in the EU during 2025, ENISA observed that cybercriminals “increasingly targeted third-party providers, such as digital services”, most likely in order to make their attacks more efficient (ENISA Threat Landscape 2026, September 2026). An IT service company holds exactly this kind of position. A single stolen admin login can lead into the systems of several clients.
A call from “IT support”
ENISA describes vishing campaigns in which attackers impersonate IT personnel to steal single sign-on credentials and codes for multi-factor authentication. An advisory by CISA and partner agencies, updated in July 2025, also describes callers who persuade help desk staff to reset passwords or MFA. Service desks that handle such requests for clients hear these calls on an ordinary working day.
Code and credentials in the wrong place
Developers work with repository access, cloud consoles and tokens that attackers want. A login page copied from a familiar tool is enough to capture them. Client code pasted into an unapproved AI tool creates a different risk: it becomes shadow IT that nobody has checked.
Lures that look like daily work
It might be a ticket notification, an invitation to a shared document, a licence renewal or a string of login prompts that only stops once someone approves it. Attacks on IT teams copy the tools they use all day. An MFA fatigue attack relies on exactly this routine.
COMPLIANCE AND AUDIT-READINESS
What NIS2, the Cyber Resilience Act and ISO/IEC 27001 expect from people
Many IT service companies answer to several frameworks at once, and to clients who ask for proof.
Your clients’ supply chain includes you
IT service companies that run client systems or cloud services can fall within the scope of NIS2 and its training duties. Clients under NIS2 or DORA also check how their providers train people.
24 hours to raise the alarm
Since 11 September 2026, the Cyber Resilience Act has required manufacturers to flag actively exploited vulnerabilities and severe incidents within 24 hours. That needs people who report problems quickly.
Awareness is on every checklist
ISO/IEC 27001 and 27701, ISO 22301 and ISO/IEC 42001 all expect staff awareness. SoSafe is aligned with NIS2, DORA and ISO/IEC 27001 and helps you demonstrate behaviour change.


WHO GETS TRAINED
Role-based training for cyber security in IT services
Admins and engineers
People with privileged access get more depth: remote access to client systems, handling credentials, and what to do in the first minutes of an incident. Short lessons fit between tickets and deployments.
Developers
Developers have content of their own within the track for IT specialists. To an attacker, a repository login or an access token is worth as much as an admin password. A suspected vulnerability that someone reports early leaves more time to act.
At the service desk
Training covers technical support scams and fake account recovery requests. Your own procedure for verifying a caller before a password or MFA reset can become a lesson too.
Consultants, freelancers and leadership
Consultants work with client data on site and on the move. Freelancers and subcontractors can join without a company email address. Managers get shorter content that starts from their responsibilities for cyber risk.
Lessons in a few minutes
Content adapts to prior knowledge and risk profile, and you assign it by role or group. Each lesson takes one to eight minutes, on a desktop or a phone.
From reported email to simulation
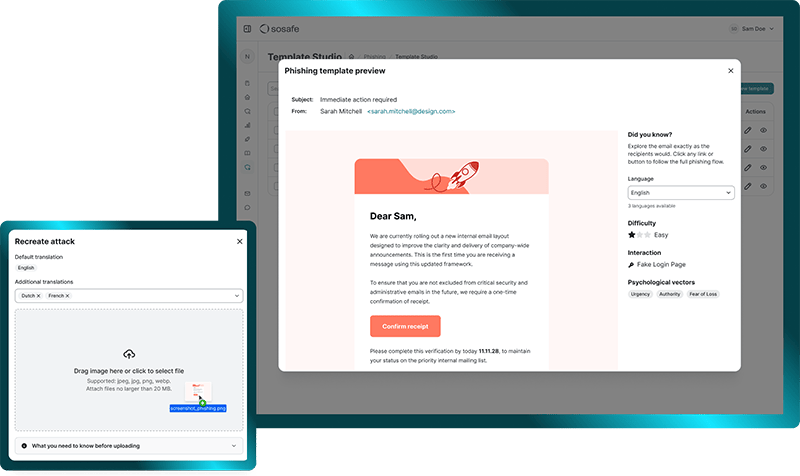
When a phishing email reaches your organisation, such as a fake ticket notification, the security team can rebuild it as a simulation in a few minutes and send it to the people it targeted.
A practice call in the browser
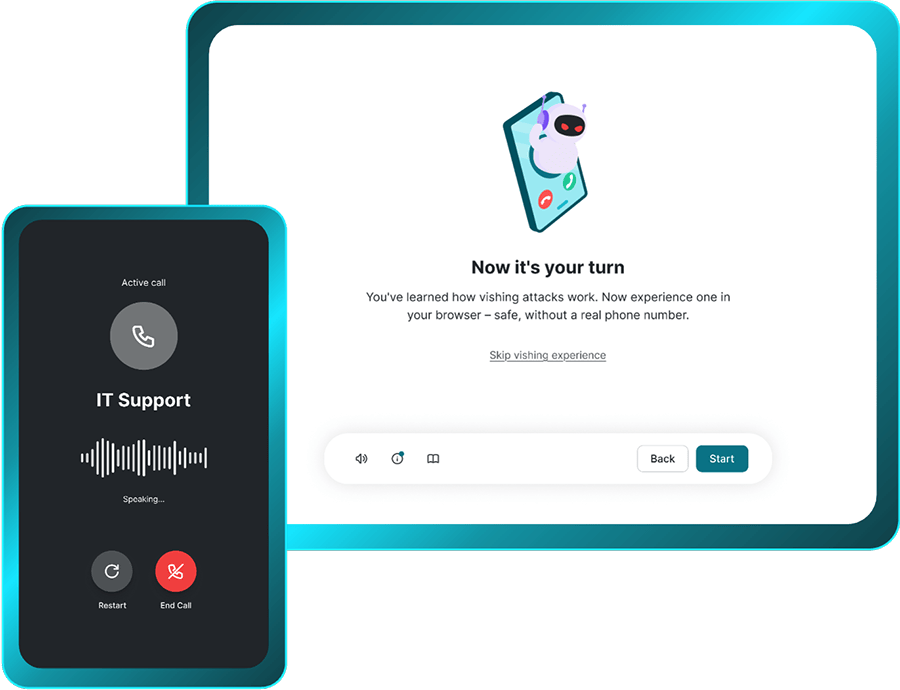
The Interactive Vishing Lesson ends with a realistic call in the browser, such as a “colleague” who urgently needs a password reset. No phone numbers are needed. It builds the habit of checking but records no failure rate.
One click to report
The report button sits in the email client. One click sends a suspicious message to a single triage queue, where the security team reviews all reports together and decides what needs action.
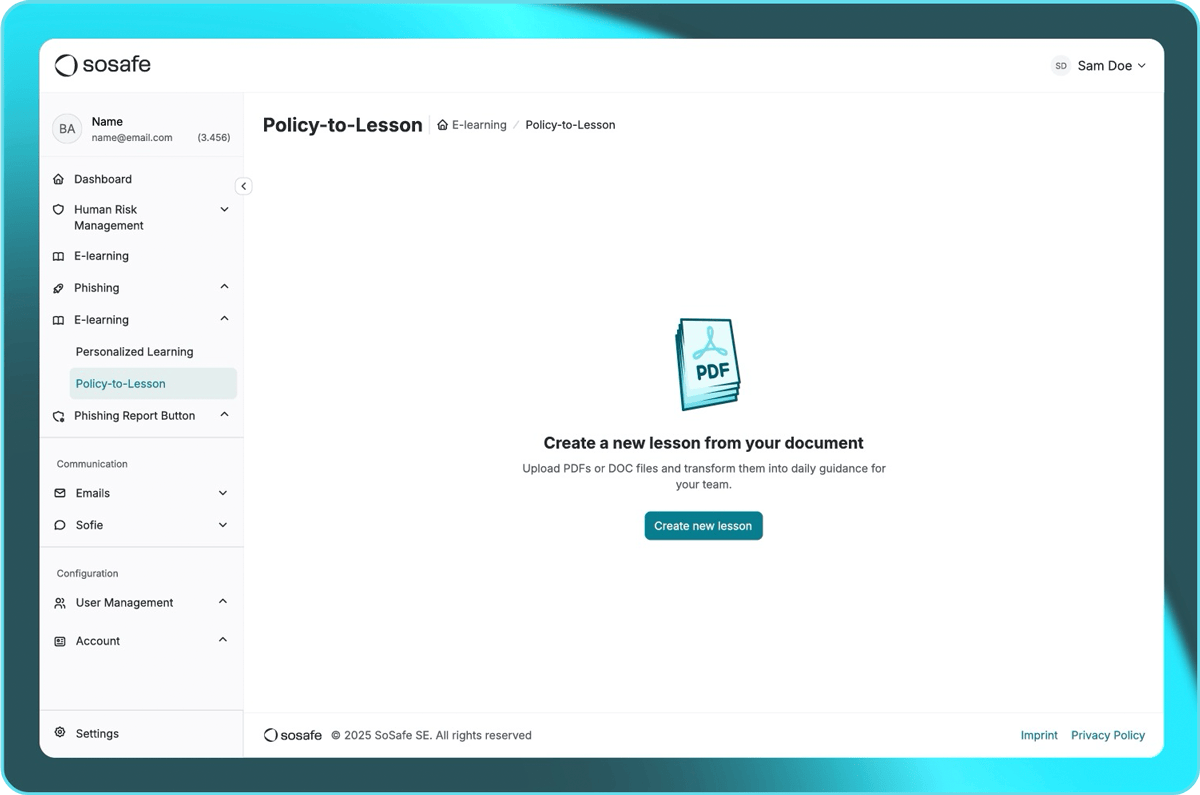
Your own rules as lessons
Upload a policy as a PDF, such as your rule for client data in AI tools. Policy-to-Lesson drafts an editable lesson that you review before publishing and translate into your enabled languages.
Evidence for audits and clients
Export training and simulation results to document your programme for audits and client reviews. The Human Security Index shows how human risk develops over time.
“Having one solution improved our efficiency by at least 30% and made the technical setup simpler. […] I could stand behind the desk and preach about security culture, but having experts create lessons and templates is extremely beneficial. It would take us a lot of time to develop the materials ourselves, and the quality wouldn’t come close to what SoSafe offers with gamification, quizzes, and videos.”
Roald Roos
CISO at Fellowmind, a full-service Microsoft partner with more than 2,000 professionals across five European countries
88%
knowledge retention after 12 months
90%
reduction in risky interactions
80%
reporting threats within 12 months
15 min
per week to run the full programme

Measurable impact for IT service companies
Clients and auditors expect evidence that behaviour changes, not only that training took place. SoSafe is trusted by more than 6,000 organisations worldwide, and the figures below come from aggregated data across their live programmes in all sectors.
Connected to the tools IT service companies already use
SoSafe connects with your identity provider, your HR system for user provisioning, your ticketing tools and the collaboration tools your teams work in. If you run your own learning platform, lessons can be exported as SCORM packages.
Integrations
See all the integrations


Compliance
See all our certificationsGDPR Compliant
German Engineered
EU Hosted
IT services cyber security FAQs
See SoSafe at work in IT services




 Reports
 Guides
 Blog
 Glossary
 Perks
 Customer stories
 Webinars
 Replays
 Podcast
 All events
 Signal Security Summit
 Danger Lab
 Careers
 News & press
 Contact
