Product
How to turn reported threats into real-time workforce protection
When an employee reports a phishing email, the SOC investigates it, blocks the malicious elements and closes the incident. That handles the immediate threat.
But what happens when the attacker changes a few details and sends the same tactic to another 50 employees? Will they spot it?
Not necessarily. Security has seen how the attack works, but the rest of the workforce has not. That is where the workflow needs to change. The insight from a real attack should not stop with the incident, but help prepare everyone else for what comes next.
Useful threat intelligence gets stuck in triage
Getting employees to report suspicious emails consistently creates a problem of its own: they report a lot of them, and most turn out to be harmless. Lean teams still have to work through these newsletters, internal updates, spam and legitimate supplier messages before finding the handful that matter.
Three figures show where the process starts to drag:
- 3 in every 100 user reports are actual threats. The other 97% are legitimate messages or everyday inbox noise that analysts still have to review.
- 13 days is the median response time. A reported message can sit in the queue for nearly 2 weeks before someone acts on it.
- 19 days to update workforce defences. By then, the tactic may have had almost 3 weeks to circulate.
Attackers, of course, have no reason to wait. If an impersonation, request or piece of wording works, they can reuse it with a different domain, another department or a slightly better story.
Awareness programmes move more slowly. Planned simulations and template libraries are useful for broad coverage and basic habits, but they cannot cover every tactic attackers will use against employees.
Reported attacks, on the other hand, give you something concrete to work with. They show which brands are being impersonated, which authority claims are being used and which details attackers think employees will trust.
The difficulty is getting that material out of the SOC and into training without creating another manual job. Links need to be neutralised, personal data removed and the message rebuilt safely. When triage is already taking up the team’s time, that work is easy to postpone.
Turn a confirmed threat into training in a single workflow
If your current triage setup already works, SoSafe can fit around it. The workflow supports 3 steps:
- Find the reports worth acting on. SoSafe Threat Inbox uses AI to filter false positives and surface higher-priority reports, helping administrators focus on genuine risks.
- Reuse the attack without the risk. SoSafe Recreate Attack turns the investigated email into a safe simulation starting point while keeping the context that made the original convincing.
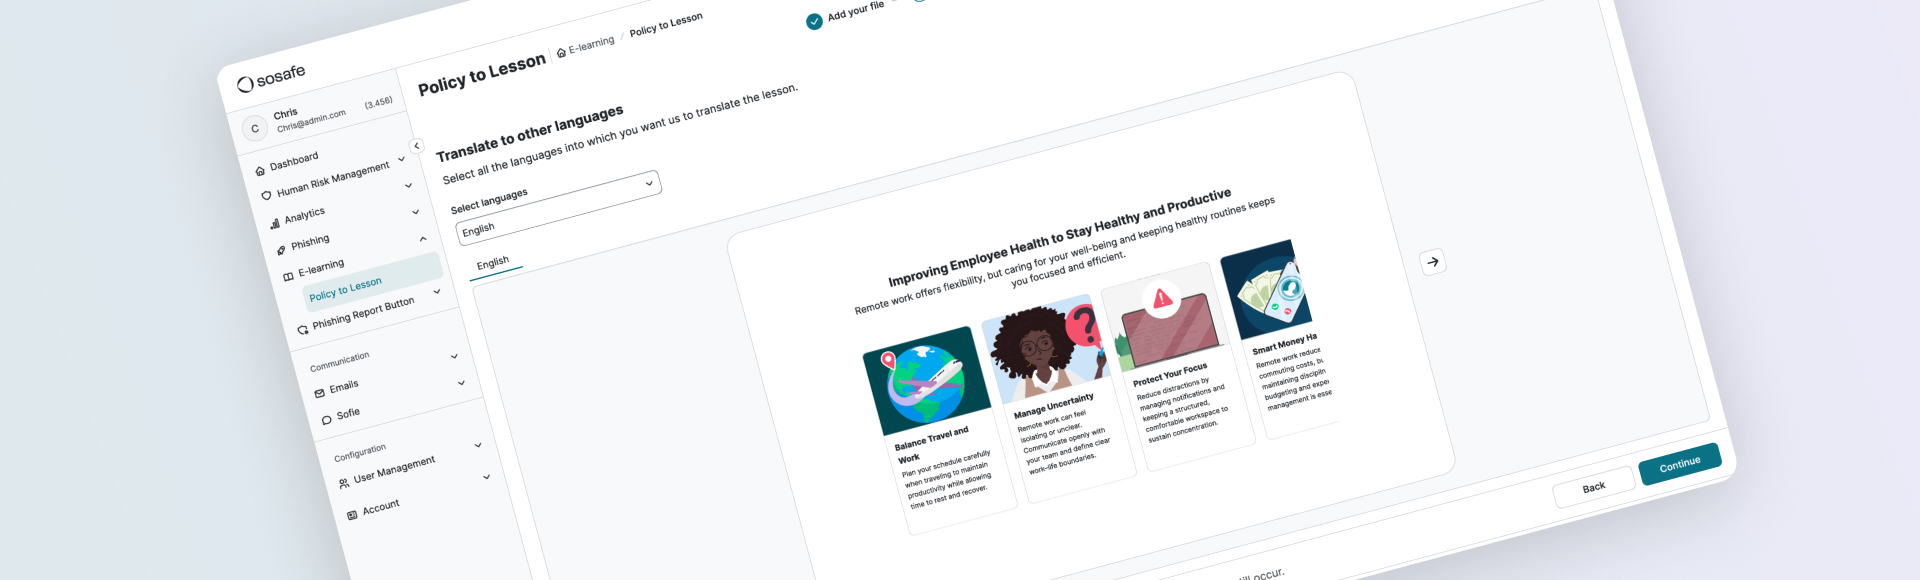
- Keep control of the final version. SoSafe Template Studio lets administrators review, refine and localise the content before it reaches employees.
You can still use template libraries for planned coverage. This adds a faster layer for the attacks no one could schedule in advance.
Instead of copying, sanitising and rebuilding a message across separate steps, teams can move from a confirmed threat to a deployed simulation in around an hour.
Train for the attack that just happened
The goal is not more training, but more relevant training. When simulations reflect threats the organisation is seeing now, awareness stays closer to operational risk and employees practise against what they are actually likely to face.
If you want to see how SoSafe can turn live incident intelligence into timely employee training, book a SoSafe demo.
You might also be interested in:
 6 min read
Do you want to stay ahead of the cyber game?
Sign up for our newsletter to receive the latest cyber security articles, events, and resources. No spam, only content that truly matters.





 Reports
 Guides
 Blog
 Glossary
 Perks
 Customer stories
 Webinars
 Replays
 Podcast
 All events
 Signal Security Summit
 Danger Lab
 Careers
 News & press
 Contact
